Code. Context. Confidence.

See the risk.
Follow the evidence.
Ship with confidence.

Three security agents for the way you build. Review pull requests, understand your codebase, and verify what matters against a live target.

Pull request reviewsRepository investigationsLive verification
Security in the developer workflow
Review / account.tsPULL REQUESTsrc / routes / account.ts12router.get('/account/:id', async (req, res) => {13 const accountId = req.params.id;14 const account = await db.accounts.findOne({15 id: accountId16 });17 return res.json(account);18});Missing resource authorizationHIGHCheck ownership before returning the account.Add the authenticated user's ID to the lookup.

01 / Your security team, extended

The right agent.
At the right moment.

A change, a codebase, and a live application each need a different perspective. Choose your starting point. Go deeper when you need to.

01 / Pull request
Review / account.tsPULL REQUESTsrc / routes / account.ts12router.get('/account/:id', async (req, res) => {13 const accountId = req.params.id;14 const account = await db.accounts.findOne({15 id: accountId16 });17 return res.json(account);18});Missing resource authorizationHIGHCheck ownership before returning the account.Add the authenticated user's ID to the lookup.

PR Agent

Secure every change

Catch risky changes while the code is still in review. Give developers security feedback where they already work.

  • Review changes as pull requests open
  • Identify injection, authorization, and secret-handling issues

$30 per seat / month

Explore PR Agent
02 / Whole repository
Repository / application contextSOURCE → SINKEXPLORERsrc/ routes/ account.ts services/ account.ts storage/ query.tsAPI routeEntry pointServiceTrust boundaryQuerySensitive sinkauth.tsA connected code pathInput → service → database operation

Whitebox

Understand the whole codebase

Investigate the paths a single diff cannot reveal. Follow data across files and understand where trust boundaries break.

  • Map entry points and trust boundaries from source code
  • Trace data across files, from entry point to sink

Starting from $100 · Custom for mature applications

Explore Whitebox
03 / Live target
Live assessmentSCOPED TARGETapp.example / api / accountsASSESSMENT OBJECTIVEInvestigate cross-account accessExplore the access pathIndependently verifyPreserve the evidenceVerification evidenceREQUEST / OBSERVED RESPONSEGET /api/accounts/other-account200 OK · account data returnedAccess outside the expected boundaryEvidence supports the finding

Red Agent

Verify the real-world impact

Assess a running target against a defined objective. Investigate potential weaknesses and report findings supported by proof.

  • Start with a target and an assessment objective
  • Use specialist agents to investigate and verify

Custom pricing for your assessment

Explore Red Agent

02 / Follow the flow

From a question
to a clear next step.

Watch the connections. See how each agent turns its input into evidence your team can act on.

Pull request

Secure every change

Catch risky changes while the code is still in review. Give developers security feedback where they already work.

  1. 1ConnectConnect your source control and choose the repository you want to review.
  2. 2Open a PRA new pull request gives the agent a specific change to investigate.
  3. 3ReviewThe agent examines the change for security issues and explains the risk.
  4. 4ActFindings arrive as review comments so developers can address them before merging.
Explore PR Agent

PR Agent / Process overview

Review / account.tsPULL REQUESTsrc / routes / account.ts12router.get('/account/:id', async (req, res) => {13 const accountId = req.params.id;14 const account = await db.accounts.findOne({15 id: accountId16 });17 return res.json(account);18});Missing resource authorizationHIGHCheck ownership before returning the account.Add the authenticated user's ID to the lookup.
Code changeSecurity reviewReview feedback

The outcome

Inline feedback with a clear explanation and suggested fix.

Platform

One Platform. Complete Visibility.

Explore every dimension of your security posture from a single pane of glass.

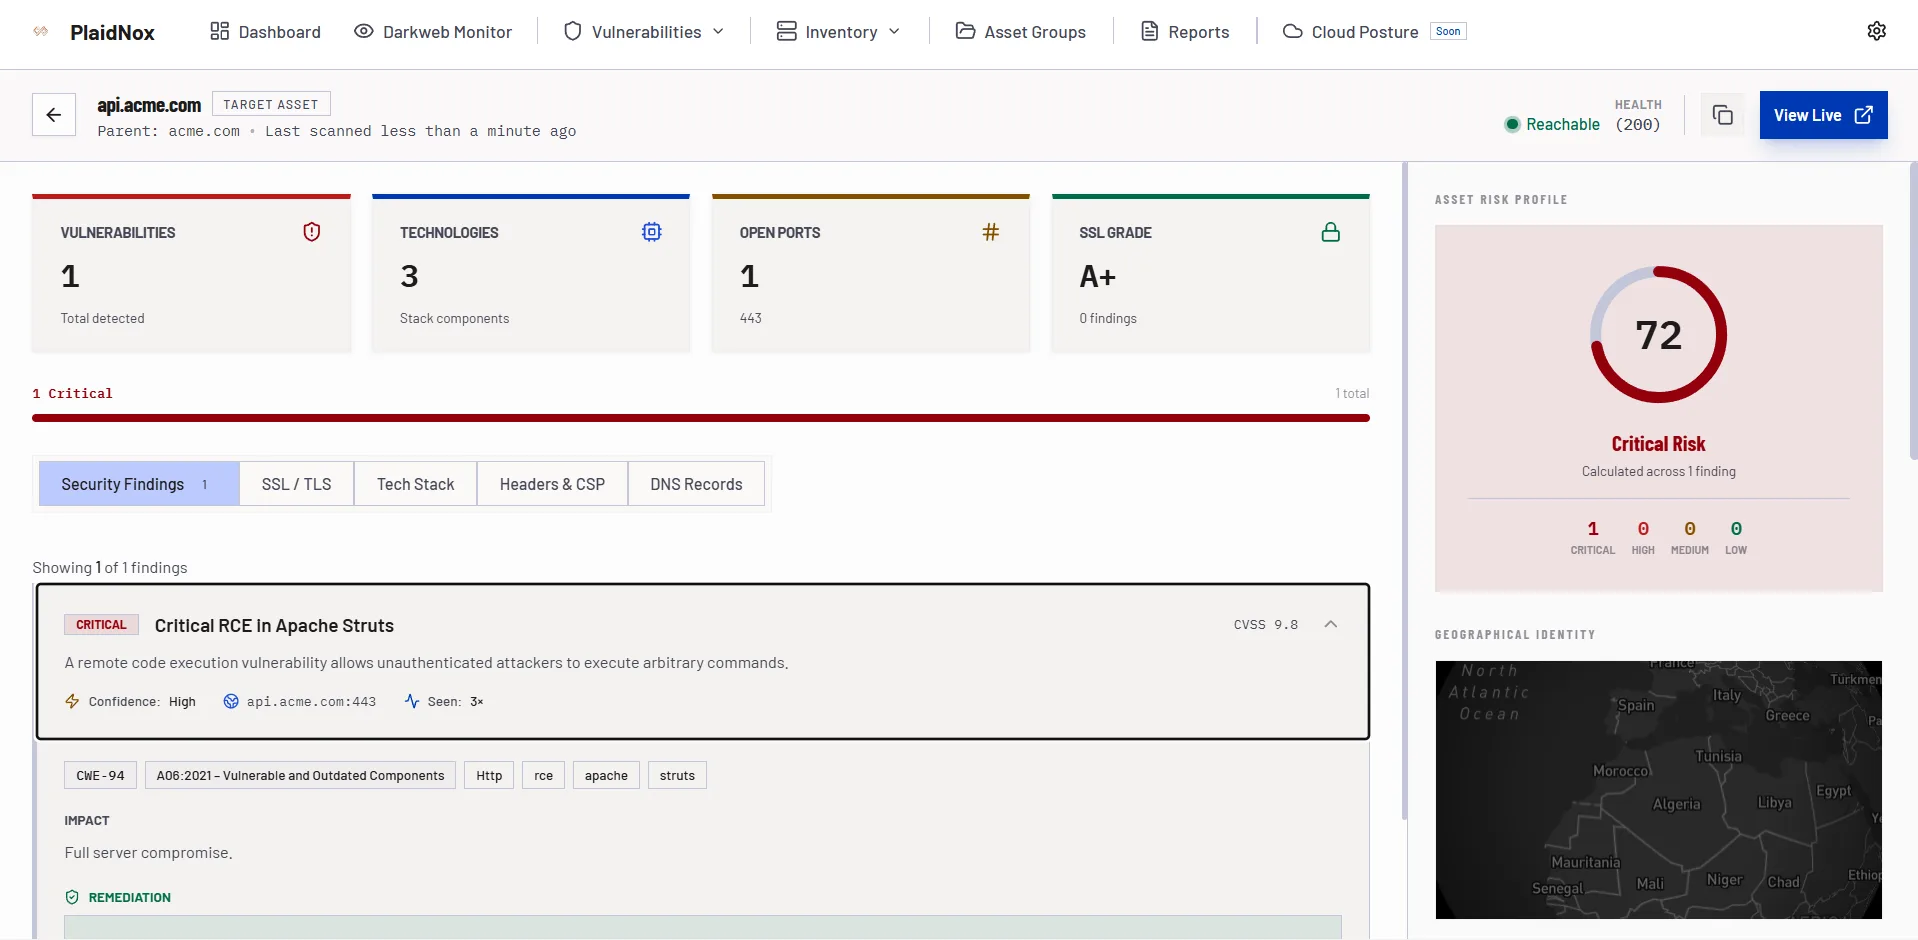
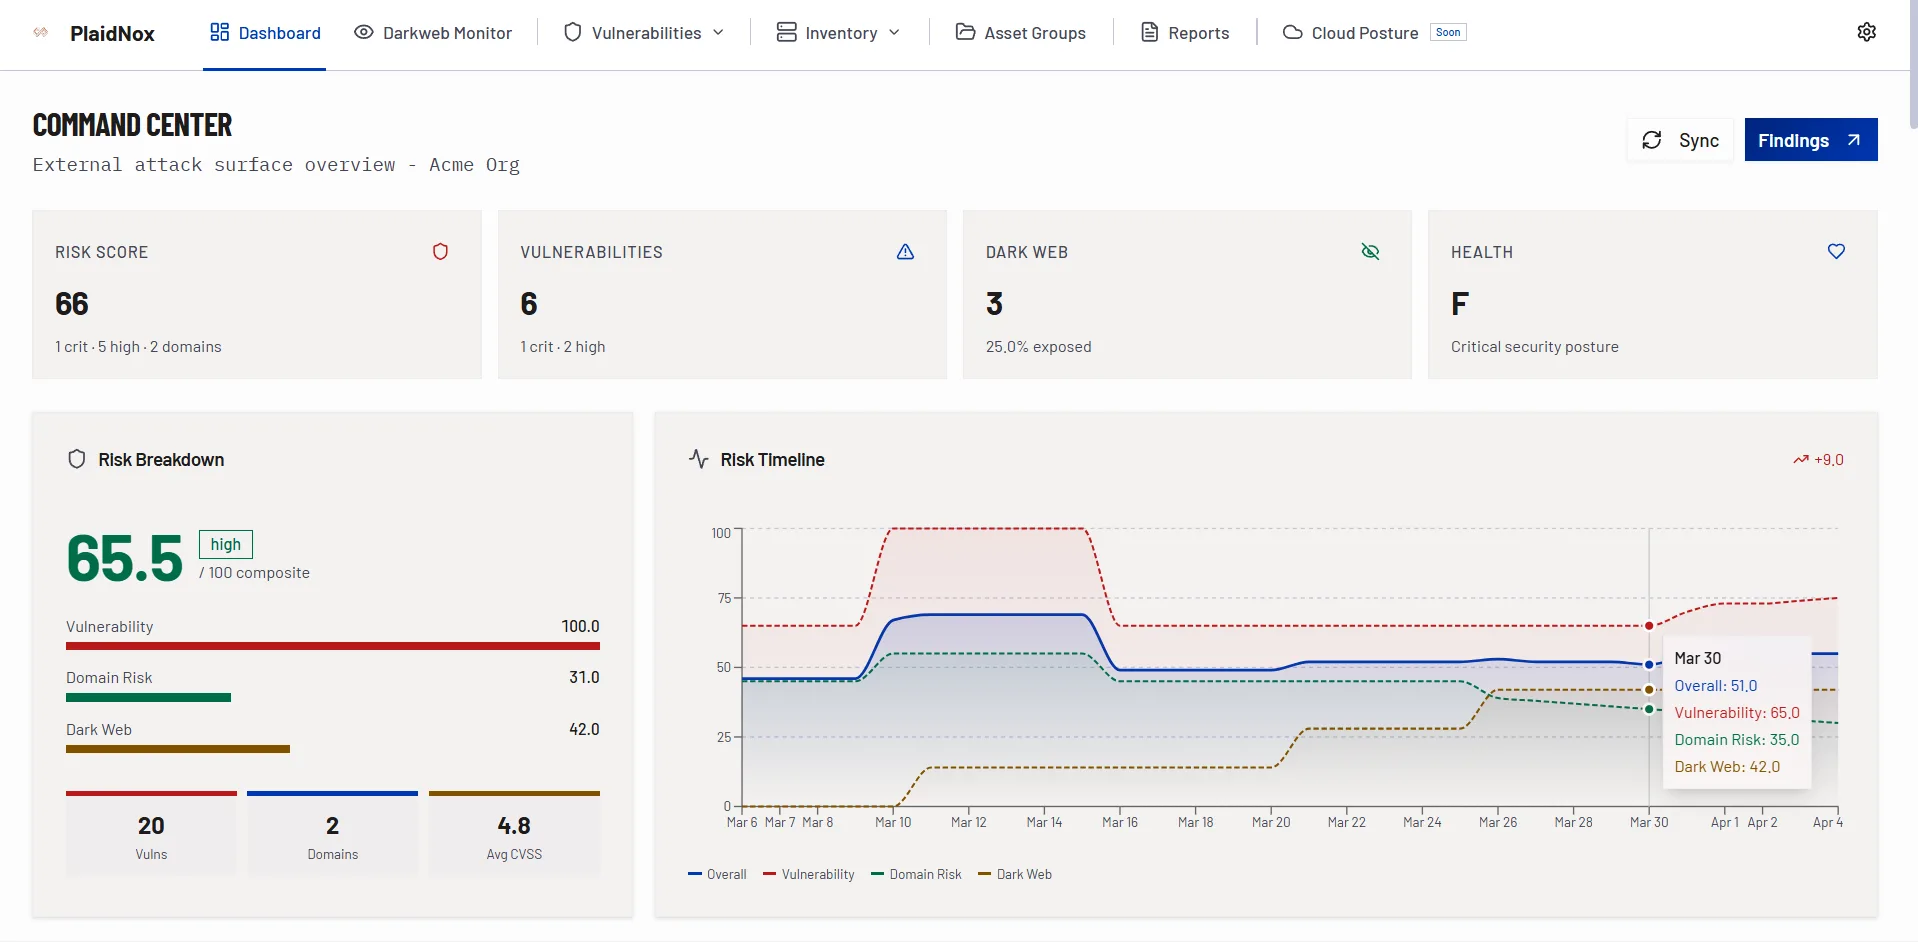
veta.plaidnox.com - Dashboard
PlaidNox Dashboard view

Executive overview with risk scores, vulnerability counts, and asset discovery stats.

Use Cases

How PlaidNox Transforms Security

veta.plaidnox.com
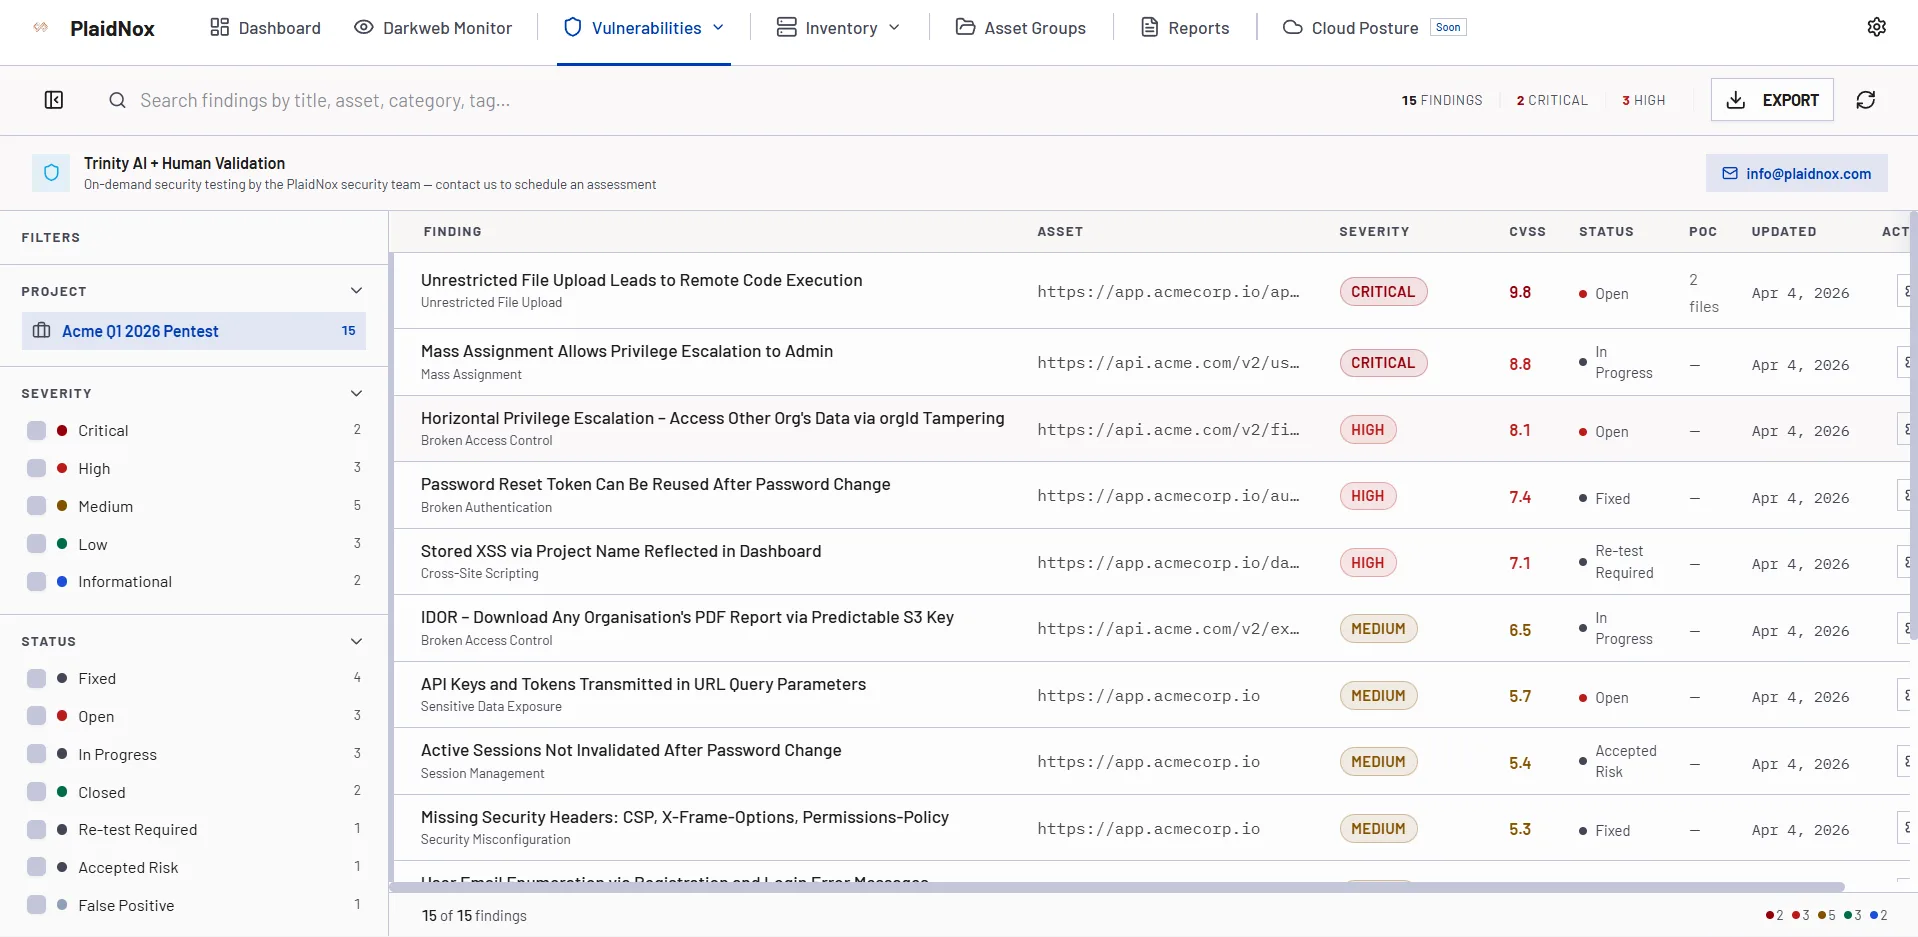
AI-Powered Penetration Testing

Automated vulnerability discovery combining AI scanning with human-expert validation. Continuous testing, not just annual snapshots. Streaming repro steps with automated retest for every finding.

Configuration & Advisory

We Help Organizations Build & Configure Security Infrastructure

From initial architecture to ongoing optimization - PlaidNox provides hands-on expertise to configure, harden, and maintain your security stack. We help organizations place security first, build Zero Trust, and improve security posture externally and internally.

01

PAM Implementation

Deploy and configure CyberArk, BeyondTrust, or Delinea. Vault credentials, enforce session recording, implement just-in-time access, and establish privileged account lifecycle governance.

02

SIEM Deployment & Tuning

Set up Splunk, Sentinel, QRadar, or Elastic SIEM. Create custom detection rules, reduce alert fatigue by 70%+, build correlation logic, and integrate threat intelligence feeds.

03

SOC Build & Optimization

Design SOC workflows, create incident response playbooks, implement SOAR automation, define escalation matrices, and establish 24/7 monitoring procedures.

04

Identity & Access Management

Configure Okta, Azure AD, Ping Identity, or ForgeRock. Implement SSO, MFA, conditional access policies, identity lifecycle automation, and access certification campaigns.

05

Firewall & Network Security

Optimize Palo Alto, Fortinet, or Check Point rules. Implement micro-segmentation, ZTNA policies, network access control, and IDS/IPS tuning.

06

Use-Case Development

Create custom detection use-cases, threat hunting queries, automated response workflows, and compliance monitoring dashboards tailored to your industry and threat landscape.
Integrations

Integrates With Your Security Stack

AWS
Azure
GCP
Jira
Slack
Discord
Teams
Zoho Cliq
Webhook
ServiceNow

Platform Highlights

Built for Security Teams, Loved by CISOs

Every view is designed to surface what matters - from real-time notifications to detailed vulnerability analysis.

veta.plaidnox.com
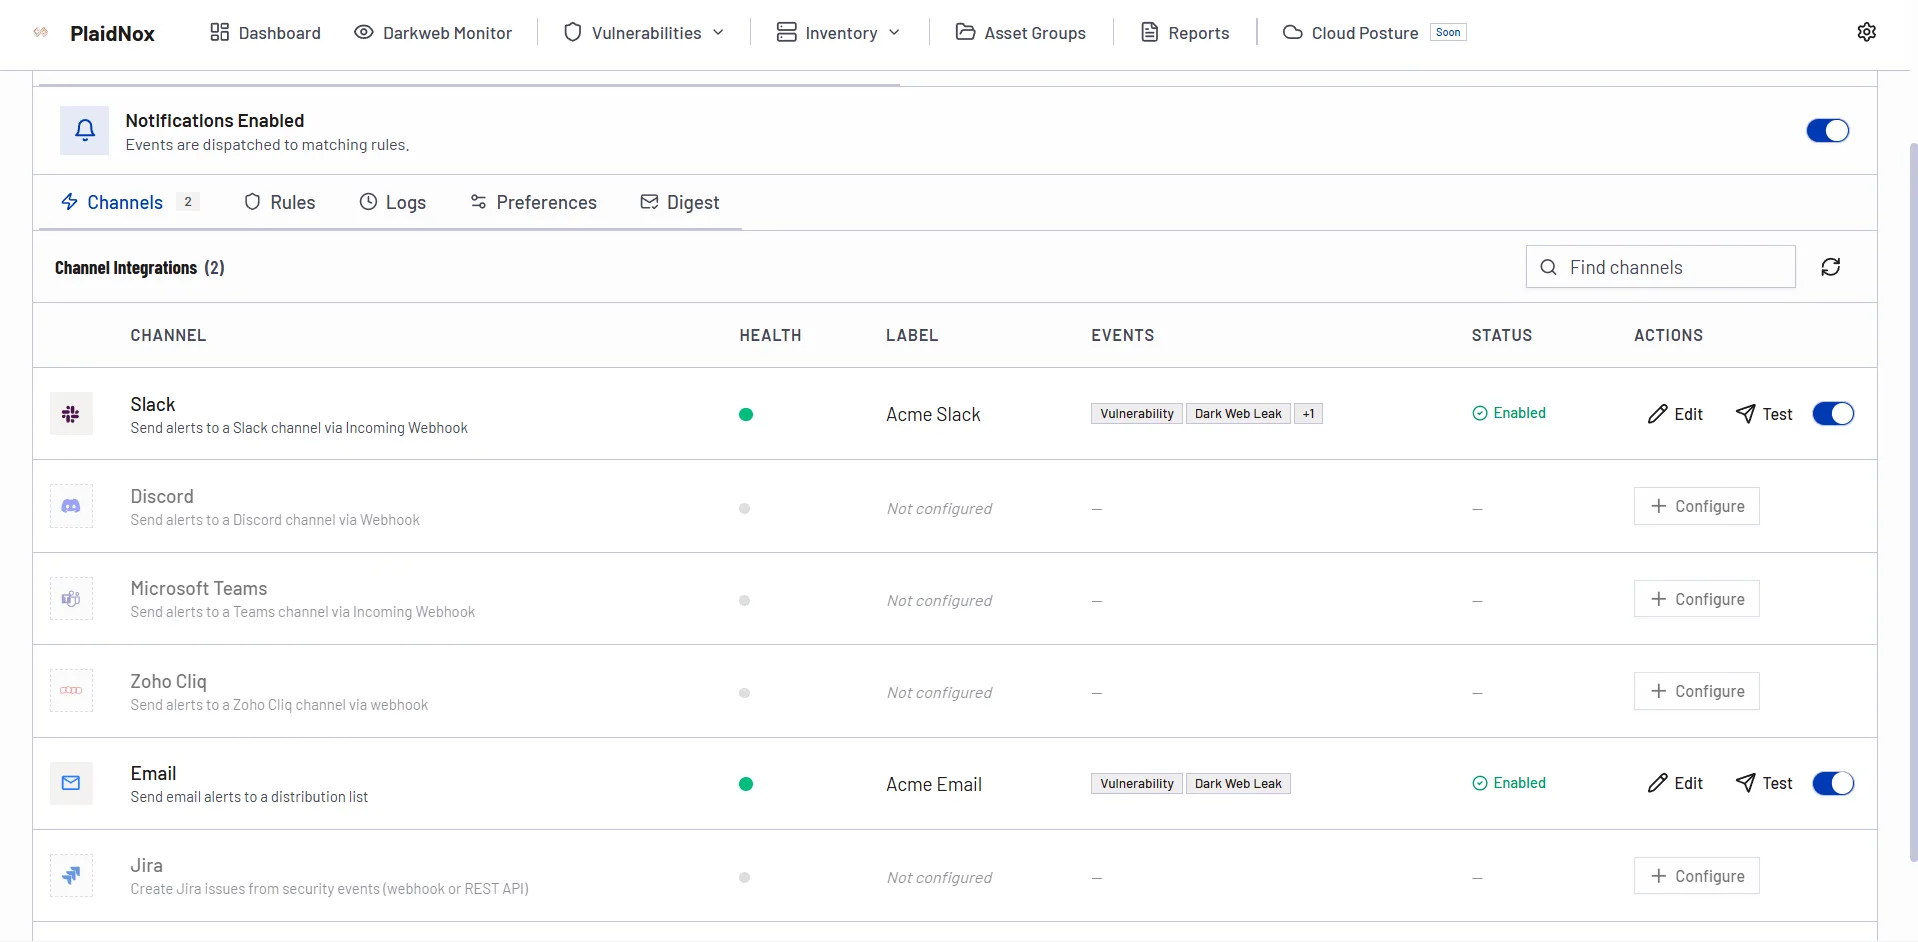
Real-Time Notifications

Real-Time Notifications

Stay on top of critical findings, remediation deadlines, and team activity with intelligent notification feeds.

veta.plaidnox.com
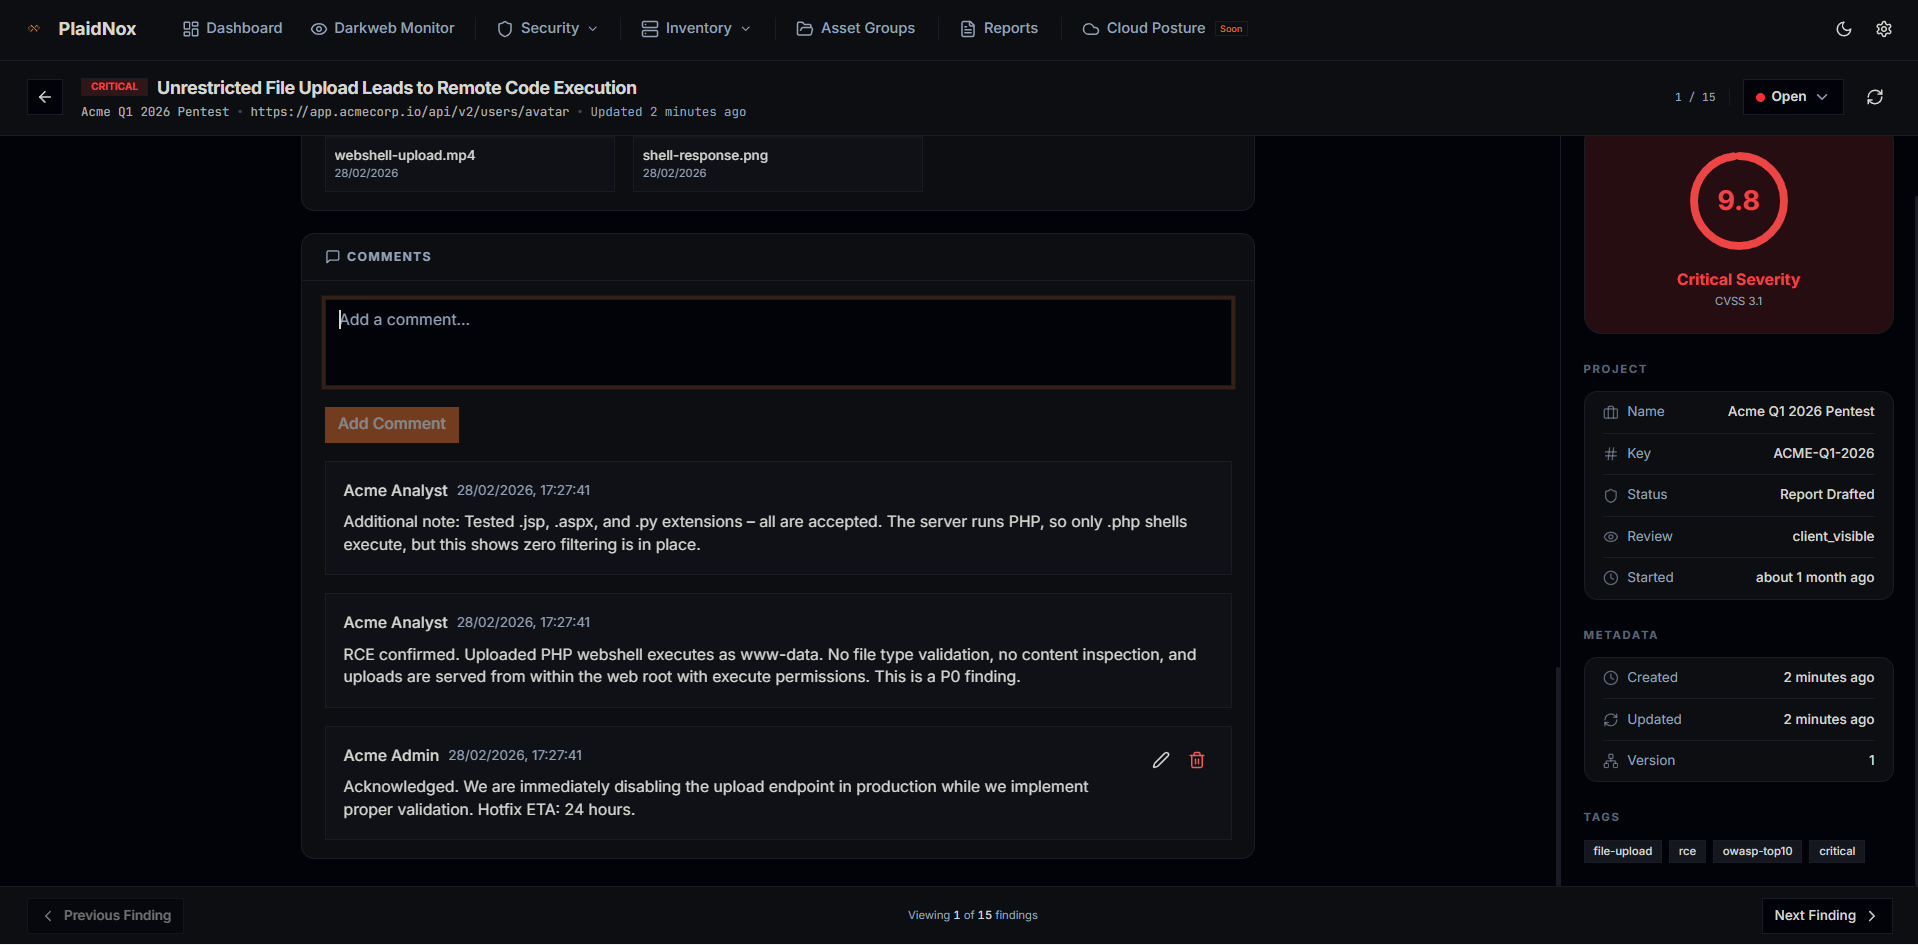
Collaborative Workflow

Collaborative Workflow

Comment on findings, assign tasks, and coordinate remediation directly within the platform.

veta.plaidnox.com
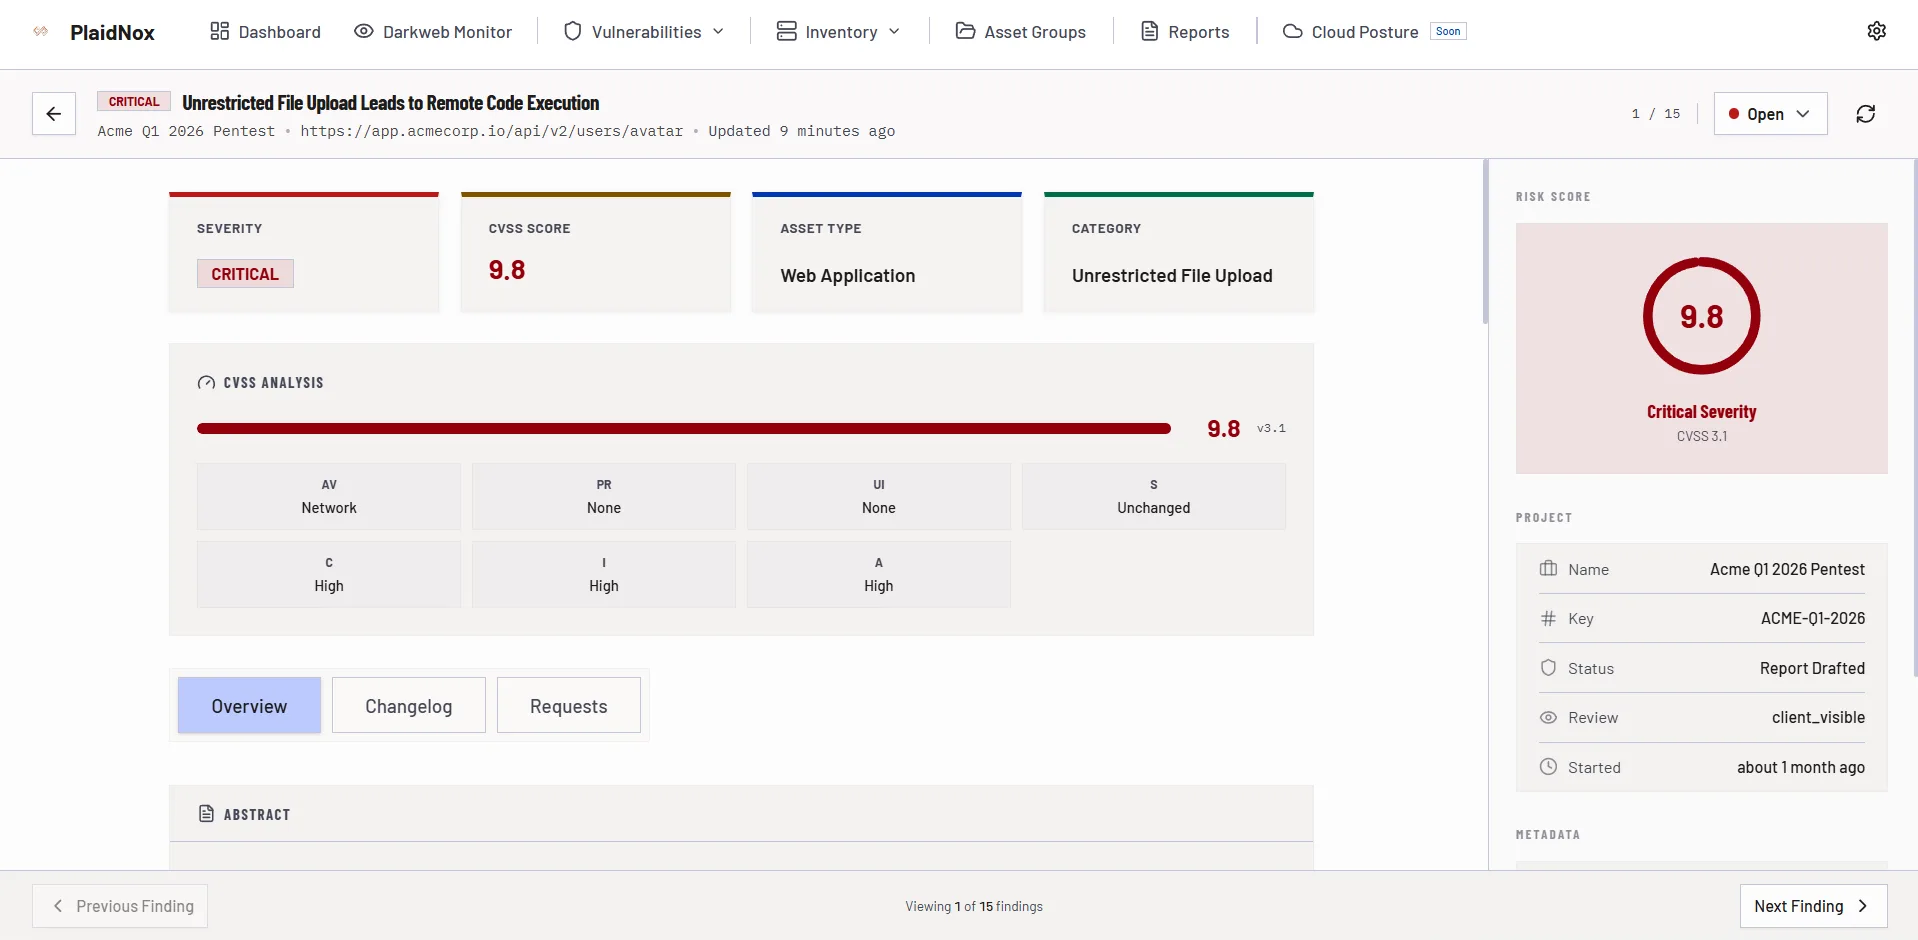
Vulnerability Deep-Dive

Vulnerability Deep-Dive

Detailed vulnerability analysis with CVSS scoring, exploit availability, and step-by-step remediation guidance.

veta.plaidnox.com
Investigation & Triage

Investigation & Triage

Correlated attack paths, evidence collection, and guided investigation workflows for faster response.

Ready to Strengthen Your Security Posture?

Free scoping call - no obligationReports you can act on immediately